Engineering Service
Controlled Scope
Targets, test windows, access, exclusions and escalation paths are agreed before active security testing begins.
Engineering Service
Azeosoft helps organizations identify, validate and reduce security risk across web applications, APIs, mobile apps, cloud infrastructure and internal systems through evidence-led testing and investigation.
Service Overview
Security assessments, penetration testing, DAST, incident investigation and remediation validation. The work is planned with enough structure to reduce uncertainty while leaving room for iteration, stakeholder feedback and production realities.
Targets, test windows, access, exclusions and escalation paths are agreed before active security testing begins.
Automated signals are manually reviewed so the report focuses on credible weaknesses, attack paths and business impact.
Findings include practical fix guidance and can be retested to confirm resolution and document residual risk.
Engineering Depth
Each engagement is shaped around architecture, security, testing, deployment and production operation rather than a single framework choice. The capability mix is adjusted to match the product stage, codebase maturity and delivery pressure.
Detailed Service Sections
Each service area is broken into practical workstreams so buyers can understand what is planned, built, validated and handed over.
We combine automated discovery with manual validation to identify exploitable weaknesses and realistic attack paths.
Running applications and delivery pipelines are assessed for security flaws across code, dependencies, configuration and exposed behavior.
Suspicious events are investigated through logs, system evidence and activity timelines to understand entry points, scope and root cause.
Cloud environments, identity controls, networks, containers and platform configurations are reviewed for dangerous exposure and privilege paths.
We map trust boundaries, sensitive assets, abuse cases and likely attack paths before they become expensive production weaknesses.
Findings are translated into practical engineering actions, then retested to verify fixes and identify residual risk.
Delivery Approach
The engagement is split into practical stages so planning, engineering, validation and operational handoff remain visible throughout the work.
Define authorized targets, test depth, credentials, time windows, exclusions, contacts and evidence-handling requirements.
Map assets, technologies, data flows, trust boundaries, attack surface and high-risk abuse cases.
Run appropriate automated and manual tests across applications, APIs, mobile clients, cloud services and infrastructure.
Reproduce credible issues, connect related weaknesses into attack paths and investigate relevant logs or system evidence.
Deliver risk-ranked findings with evidence, impact, reproduction guidance and practical remediation actions.
Verify completed fixes, document remaining exposure and provide closure evidence for stakeholders.
Architecture & Flow
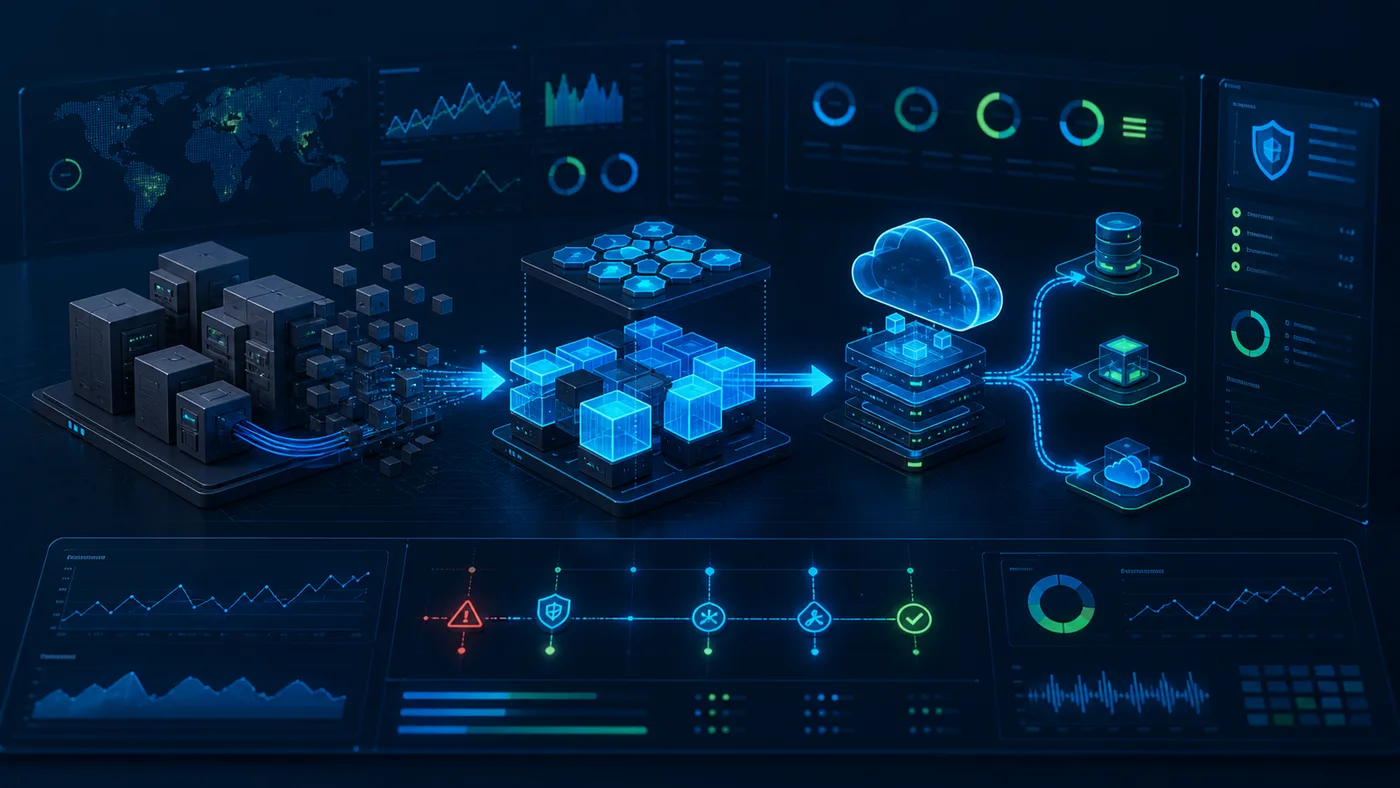
The working model is intentionally explicit: decisions, dependencies, environments, reviews and production signals are represented before the system is treated as finished.
Methodology & Tooling
Standards and tools support coverage, but experienced validation determines what is exploitable, how it affects the business and what should be fixed first.
Validated findings include reproducible evidence, affected assets and the conditions required for exploitation.
Severity considers exploitability, exposure, data sensitivity and business impact rather than scanner score alone.
Reports give engineering and infrastructure teams clear remediation actions, ownership context and retest status.
Expected Outcomes
The goal is not only to complete tickets. The work should leave the product, platform or team stronger, easier to operate and better prepared for the next stage.
Talk to Engineering
From the first architecture decision to production deployment and global scaling, Azeosoft Engineering can help design, build and operate the platform.